How Maryland Cybersecurity Teams Reconcile Duplicate Device Findings in Salesforce
Why Do Duplicate Device Vulnerability Findings Matter to Maryland Cybersecurity Teams?
In this anonymized composite scenario, a Maryland cybersecurity services team receives the same device vulnerability through a scanner feed and an advisory import, creating two Salesforce custom Vulnerability Finding rows for one affected device and CVE. An illustrative 15,000-row review shows how the admin separates duplicate findings from distinct devices and scan observations, then uses preview, backup, controlled batches, bulk undo, and restore for supported CRM corrections. This is not a named customer result.
Why the Same Device and CVE Can Produce Two CRM Findings
CISA’s Continuous Diagnostics and Mitigation technical-capabilities guidance explicitly includes duplicate vulnerability reporting for a given device among its false-positive examples. NIST’s National Vulnerability Database explains that a CVE identifies a unique vulnerability, while affected product versions still determine applicability. Together, those sources support checking the device plus CVE before treating two imported Salesforce finding rows as separate open risks; the CVE alone is not a unique device finding. The Maryland Department of Commerce’s 2025 international trade report identifies cybersecurity as a state strength, and the Cybersecurity Association of Maryland describes local government and private-sector cyber work. That local setting makes reliable finding counts useful to Maryland teams, but neither source measures duplicates in their Salesforce orgs. CISA’s device-level warning is the evidence for this specific failure mode.
Use Case: One Device and CVE Appears Twice in Salesforce
A Maryland managed-security team uses a custom Salesforce Vulnerability Finding object to track customer remediation follow-up. The scanner creates a row keyed by its proprietary finding ID. A separate advisory feed creates a second row keyed by advisory ID. Both describe the same CVE on the same managed device, but their import keys do not match. An illustrative customer report now counts two open findings and sends two follow-up tasks. The original scan and advisory are still distinct pieces of source evidence, even when the current CRM finding should be one reviewed work item.
The reviewer verifies the customer tenant, stable asset ID, CVE, affected product and version, observation time, and scan status. A hostname or IP address alone can change or be reused. The same CVE on two devices remains two device findings. Two scans on different dates remain separate observations and may show a change in remediation state. A shared CVE also does not prove that a particular product version is affected. The approved CRM representation can point to both source observations without counting the same confirmed device-level finding twice.
| Record grain | Verify | Keep separate when |
|---|---|---|
| Device vulnerability finding | Customer tenant, stable asset ID, CVE, affected version, and reviewed status | Asset identity or affected version differs. |
| Scanner or advisory observation | Source ID, observation time, evidence, and import lineage | It is a distinct scan or advisory event, even if attached to one finding. |
| Remediation task | Assigned owner, due date, and verified finding relationship | The work belongs to a different device or customer. |
How the Admin Profiles and Cleans the Finding Rows
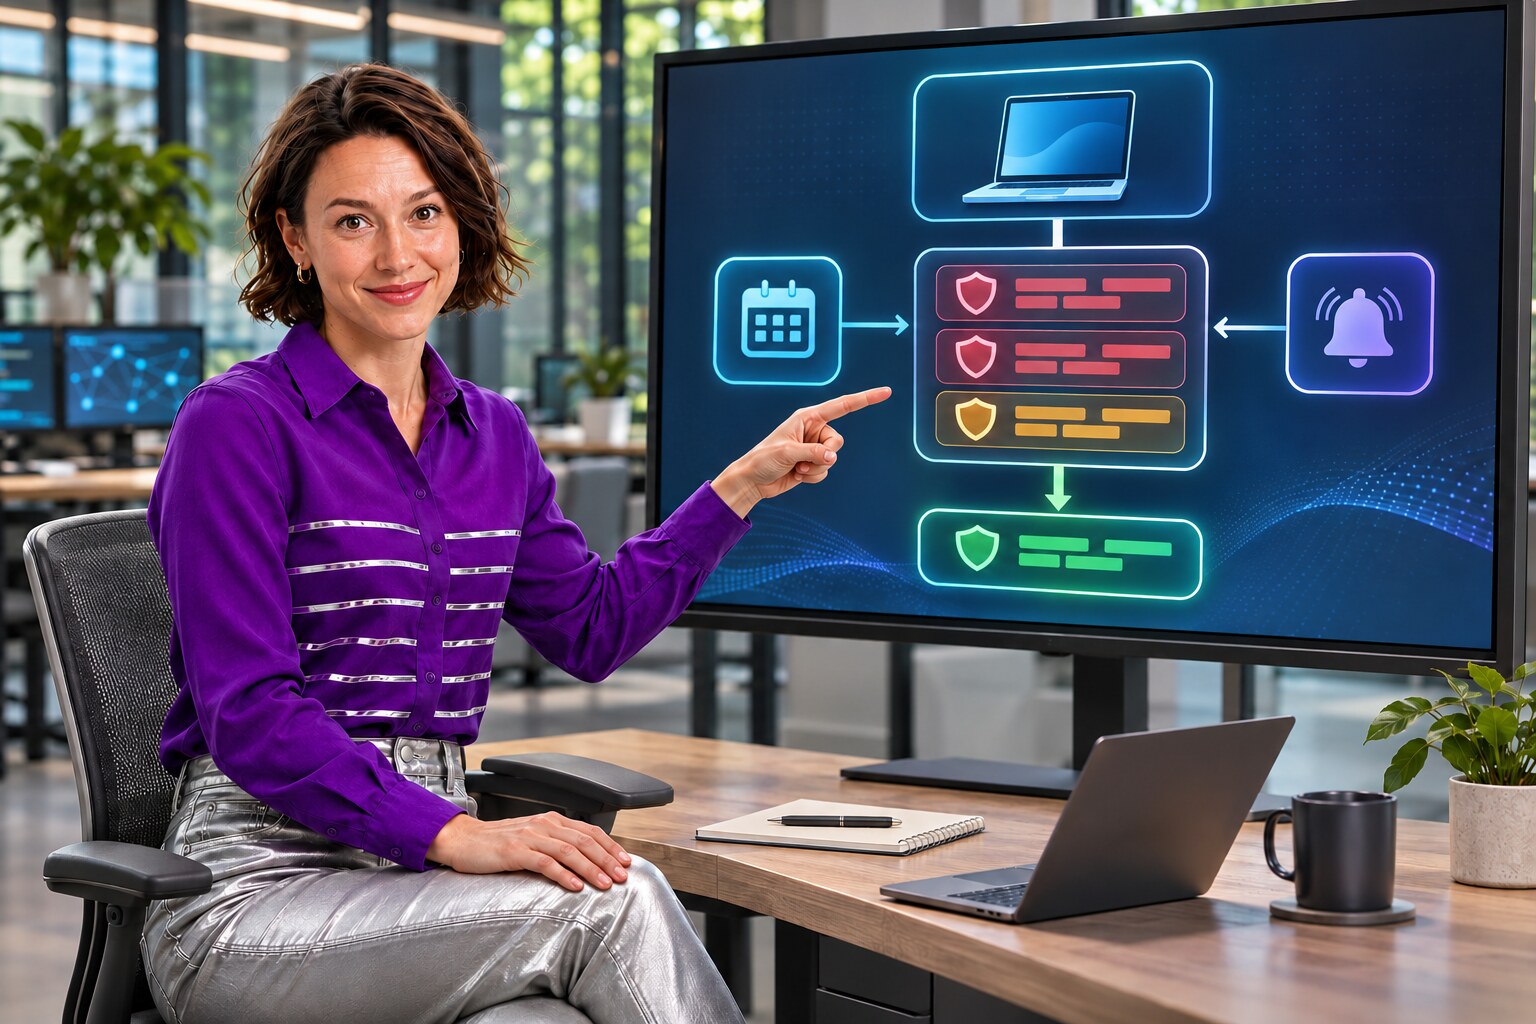
- Bound the review. Export an illustrative 15,000 affected Salesforce rows with record ID, tenant, asset ID, hostname, CVE, product version, source observation ID, status, owner, and last update. Record baseline counts by verified device and CVE, plus unresolved identity exceptions.
- Surface candidates in ZaapIT. Normalize CVE and asset-ID formatting for comparison, then filter potential same-device and same-CVE rows. Keep raw source IDs and timestamps visible. Similar titles or IP addresses trigger review, not an automatic merge.
- Approve the source-of-truth mapping. A security analyst checks the asset inventory, scanner evidence, version applicability, and current remediation state. The approved CRM finding retains references to both observations; separate devices and later independent findings stay separate. Do not copy a closed status from one stale feed over a newer confirmed open result.
- Preview and protect changes. Preview the approved Salesforce field and relationship updates, back up affected rows and old values, run a small controlled batch, validate it, then expand by batch. Use ZaapIT bulk undo and restore for supported CRM changes if the mapping or filter proves wrong. A deletion or object merge requires its own tested recovery plan.
- Prevent new duplicates. Align future upserts to an approved tenant, stable asset, and CVE key while preserving separate observation IDs. Route missing asset identities or version conflicts to the security team rather than silently creating or collapsing findings.
Salesforce Help says custom-object imports can match by name, Salesforce ID, or external ID and advises standardizing external IDs. Salesforce’s duplicate-job guidance says jobs can identify custom-object duplicates but do not provide native compare-and-merge for those records. Neither feature decides device identity, version applicability, or remediation status for the security team.
Validate One Work Item Without Losing Scan History
For each batch, reconcile distinct verified tenant–asset–CVE findings against the security team’s approved exception list. Sample the original scanner and advisory IDs, confirm that source observations still trace to the correct CRM finding, and check that separate devices are not collapsed. Compare open, closed, and awaiting-verification counts with the authoritative security system. A lower row count or fewer tasks is not proof that exposure was removed.
Test bulk undo or restore on a small approved set of supported Salesforce changes and compare recovered fields and relationships with the backup. The team separately verifies any security-system status correction. All counts and outcomes here are examples, not measured ZaapIT customer results.
Make Device Finding Cleanup Reviewable
Use ZaapIT to inspect candidate Salesforce finding duplicates, preview security-team-approved updates, retain an affected-row backup, and test bulk undo and restore for supported CRM changes.
Frequently Asked Questions
Is the same CVE on two devices one finding?
No. CVE identifies the vulnerability, while each affected device requires its own verified device-level finding and remediation context.
Should two scan observations be deleted when one CRM finding is retained?
No. Preserve each original scan or advisory observation and its time and source ID. Link both to a reviewed finding when they refer to the same device-level issue.
Can a matching hostname prove two vulnerability rows are duplicates?
No. Verify tenant, stable asset identity, CVE, affected version, and source evidence. Hostnames and IP addresses can change or be reused.
Does restoring Salesforce rows change scanner remediation status?
No. Bulk undo and restore are tested for supported Salesforce changes. Security-system findings and remediation decisions require the security team’s own workflow.
Useful ZaapIT Resources
Sources
- CISA: CDM technical capabilities, device-level duplicate vulnerability reporting
- NIST: National Vulnerability Database and CVE identity
- Maryland Department of Commerce: 2025 international trade report, cybersecurity sector
- Cybersecurity Association of Maryland: Maryland cyber ecosystem
- Salesforce Help: Custom-object import matching
- Salesforce Help: Things to Know About Duplicate Jobs